Forensics & Investigations

Executive protection OSINT · Digital executive protection · Daily briefings

Executive & VIP Online Threat Monitoring

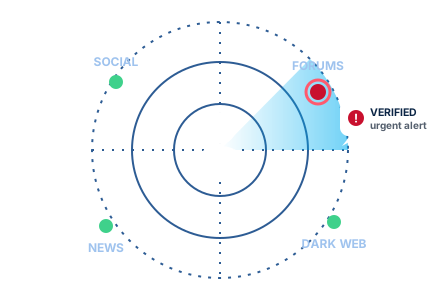
Our analysts monitor the open web, social media, news, forums and the dark web every day for threats, doxxing, impersonation and leaked personal information about the people you protect, with daily briefings and urgent alerts when something can’t wait.

Request a Confidential Consultation Call 631-982-4632

What is executive online threat monitoring?

High-profile people are discussed, criticized and sometimes targeted online every day. Most of it is noise. Some of it is not: a fake account using their name, a home address posted on a forum, a hostile post that mentions where they will be next week, or their credentials in a data dump.

Executive online threat monitoring, sometimes called digital executive protection or executive protection OSINT, is how you find those signals early. We use open-source intelligence to watch the places threats and exposures surface, our analysts verify what we find, and your security team gets a clear daily brief plus urgent alerts, so they can act before an online problem becomes a real-world one.

At a glance

  • Daily monitoring of social media, news, forums and the dark web
  • Threats, doxxing, impersonation and leaked personal information
  • Physical-safety indicators around homes, travel and appearances
  • Every finding verified by an analyst
  • Daily briefings plus urgent alerts
  • Takedown support and escalation to security teams or law enforcement

Who it’s for

Executives & board members

Leaders whose name, role or decisions draw public attention, and sometimes hostility.

Public figures

People with a public following who face impersonation, harassment and unwanted attention.

Entertainment & media leaders

Leaders whose work keeps them in the headlines and on social media every day.

Family offices & families

Principals and family members whose privacy and personal information need protecting.

Organizations & security teams

Corporate and private security teams that need a reliable online intelligence layer for the people they protect.

How it works

  1. 1

    Scope & profile setup

    We agree who and what to monitor (names, known accounts, key locations, upcoming appearances), what matters most and who gets alerted, how and when.

  2. 2

    Continuous collection

    We search social media, news, forums and the dark web every day for mentions, threats, impersonation and exposed personal information.

  3. 3

    Analyst verification

    Analysts review every finding, remove the noise and confirm what is real, relevant and credible before anything is reported.

  4. 4

    Alerts & daily brief

    You get a clear daily briefing, plus urgent alerts between briefings when something cannot wait.

  5. 5

    Response & escalation

    We preserve evidence, support takedown and platform reports, and escalate to your security team or law enforcement when needed.

What we monitor

The places online threats and exposures usually surface first.

Social media

Mentions, threats, hostile replies and harassment across major and fringe platforms.

News & publications

News stories, blogs and articles about the principal or their organization.

Forums & message boards

Discussion threads where hostile chatter, plans or personal details often surface first.

Dark web

Marketplaces, forums and leak sites where stolen data and threats are traded.

Leaked credentials

Email addresses and passwords tied to the principal appearing in data dumps.

Exposed personal information

Home addresses, phone numbers and family details posted or listed online (doxxing).

Impersonation

Fake accounts, profiles and pages using the principal’s name, photos or identity.

Physical-safety indicators

Mentions of homes, travel, events and public appearances that could signal a risk in the real world.

What our alerts look like

Each alert tells your team what we found, how serious it is, what was already done and what happens next. The cards below are examples only. “Client Principal” is a fictional subject and all details are sample data.

Example alertSample data
High

Impersonation account detected

Time
Mon 8:12 AM
Source
Social media
Subject
Client Principal
Status
Takedown requested

What we found: A new account using the principal’s name and profile photo (sample handle @clientprincipal.official) is messaging followers with “exclusive” investment offers.

Action taken: Analyst verified it is not affiliated with the principal. Evidence captured and impersonation reported to the platform.

Next step: Security team notified. We will confirm removal and watch for replacement accounts.

Example alertSample data
Critical

Home address posted on a forum

Time
Wed 1:47 AM
Source
Message board
Subject
Client Principal
Status
Escalated

What we found: A post in a public thread listed what appears to be the principal’s home address alongside hostile comments.

Action taken: Post verified and evidence preserved. Urgent alert sent to the security team.

Next step: Removal request submitted to the site. Thread under close watch for reposts.

Example alertSample data
Critical

Threatening post mentions upcoming public appearance

Time
Thu 6:30 PM
Source
Social media
Subject
Client Principal
Status
Escalated to security team

What we found: A user referenced the principal’s scheduled appearance at a sample event and posted language suggesting intent to confront them.

Action taken: Account history reviewed and evidence preserved. Urgent alert sent with recommended next steps.

Next step: Account under close monitoring. Information packaged for law enforcement if the security team decides to report it.

Example alertSample data
High

Credentials found in a dark-web dump

Time
Sat 10:05 AM
Source
Dark-web leak site
Account
principal@example.com
Status
Password reset coordinated

What we found: An email address associated with the principal appears with a password in a newly posted data dump.

Action taken: Exposure confirmed. Security team advised to change the password and confirm multi-factor sign-in.

Next step: Watching for further appearances of the same data.

Example alertSample data
Medium

Coordinated negative campaign spike

Time
Tue 3:20 PM
Source
Social media & forums
Subject
Client Principal
Status
Monitoring

What we found: A sudden rise in near-identical hostile posts about the principal, many from newly created accounts using the same sample hashtag.

Action taken: Pattern analyzed and accounts documented. No direct threats or personal information found so far.

Next step: Covered in the daily brief. Escalation if posts move toward threats or personal details.

Example alerts for illustration. Names, handles, addresses, times and events are sample data, not real client events.

A sample daily brief

Every morning your team receives a short, verified summary of the last 24 hours: what matters, what was done and what to watch. Urgent items are never held for the brief; they are sent as soon as they are verified.

Example only. “Client Principal” is fictional and all details are sample data.

Daily BriefClient PrincipalExampleSample data

Prepared: Thursday, 7:00 AM (sample) · Covers the previous 24 hours · Confidential

Overall assessment

Elevated One item was escalated overnight. No other direct threats were identified.

Priority items

  • Home address posted on a public forum. Escalated to the security team overnight; removal request submitted; thread being watched for reposts.

Items to watch

  • Hostile hashtag activity continuing at a lower level; no threats or personal details found.
  • Impersonation account reported earlier this week has been removed by the platform; no replacement found so far.

Upcoming appearances

  • Public event on Saturday (sample): no threatening content referencing the event identified. Monitoring continues through the event.

Exposure

  • No new credential or personal-information exposures since the last brief.

Recommended actions

  • Security team to review the forum item and residence plan.
  • Remind the principal’s staff not to post travel or event details in advance.

Case study

Case study · Online Threat Monitoring

Daily Online Threat Monitoring for a High-Profile Business Leader

Identifying details changed for confidentiality

1Problem

A high-profile business leader attracts a constant volume of online attention. Most of it is routine, but some of it can be hostile, and the leader’s security team needed to know, every day, whether anything being said or shared online pointed to a threat, an impersonation attempt or exposed personal information.

Searching social media, news, forums and the dark web by hand every day was not practical for the security team, and raw keyword alerts produced too much noise to act on with confidence.

2Approach

EDG began by agreeing the scope with the client’s security team: who and what to monitor, which kinds of findings matter most, and who should be contacted, and how, when something urgent comes up.

Our analysts now monitor every day across:

  • Social media platforms
  • News and online publications
  • Forums and message boards
  • Dark web sources

Every finding is reviewed and verified by an analyst before it is reported, so the security team receives confirmed, relevant information rather than raw search results.

The security team receives a daily briefing. Between briefings, urgent alerts go out for:

  • Threatening or hostile content
  • Impersonation accounts
  • Exposed personal information

3Result

The client’s security team has a consistent, analyst-verified daily view of what is being said and shared about the leader online, delivered in a format they can act on.

Urgent issues reach the security team as they are verified, without waiting for the next briefing, so they can decide on next steps quickly. The engagement is ongoing.

Facing something similar? Every conversation is confidential.

Request a Confidential Consultation Call 631-982-4632

Why principals and security teams choose EDG

Earlier warning

Threats, impersonation and exposed details are spotted online, often before they turn into real-world problems.

Verified, not noisy

Analysts confirm what matters, so your team acts on facts instead of sifting through raw search results.

One clear daily picture

A consistent daily briefing your security team and principal can read in minutes.

Fast escalation

Urgent items reach the right people as soon as they are verified, between briefings.

Evidence handled properly

Findings are captured and documented by a team with digital forensics experience, ready for platforms, attorneys or law enforcement.

Discreet and confidential

Every engagement is handled quietly, and principals are never named in our materials.

What you get

  • A monitoring scope and escalation plan agreed with you
  • Daily monitoring across social media, news, forums and the dark web
  • Analyst-verified findings, not raw search results
  • A daily briefing in an agreed format
  • Urgent alerts between briefings
  • Evidence capture, takedown and reporting support
  • Escalation support for your security team or law enforcement

Talk to us confidentially

Tell us who you need to protect and what concerns you. We will explain how monitoring would work for them, and what you would receive each day.

Request a Confidential Consultation

Call 631-982-4632

Executive threat monitoring FAQ

What is executive online threat monitoring?

It is ongoing, analyst-led monitoring of the open web, social media, news, forums and the dark web for anything that could put a specific person at risk: threats, harassment, impersonation, doxxing, leaked credentials and signs of physical-safety concerns. You receive a daily briefing and urgent alerts when something needs action.

Who needs this kind of monitoring?

Executives, board members, public figures, entertainment and media leaders, family offices and the security teams that protect them. It is useful for anyone whose public profile attracts attention, especially during controversy, major announcements, litigation or public appearances.

What is OSINT?

OSINT stands for open-source intelligence: information gathered from publicly available sources such as websites, social media, news and public forums. Our monitoring uses publicly available and lawfully accessible sources; we do not break into private accounts.

How is this different from social listening or brand monitoring tools?

Social listening is built for marketing: it tracks sentiment and trends. Executive threat monitoring is built for safety. It focuses on threats, impersonation, exposed personal information and physical-risk indicators, and every finding is reviewed by an analyst before it reaches you.

What do the daily briefings include?

A short overall assessment, priority items and what was done about them, items to watch, any mentions of upcoming appearances or travel, new exposures of personal information or credentials, and recommended actions. The format is agreed with you during setup.

What happens when something urgent is found?

An analyst verifies it and sends an urgent alert to the contacts agreed during setup, without waiting for the next briefing. The alert explains what was found, where, why it matters and the recommended next steps.

Can you get impersonation accounts or posted personal information taken down?

We document the content, preserve evidence and report it to the platform or site, and we help prepare removal requests. Final decisions about removal rest with each platform or site, so we keep monitoring and follow up.

Do you work with our security team and with law enforcement?

Yes. We deliver findings directly to your security team, and when a threat warrants it, we help package the evidence so it can be reported to law enforcement.

Can monitoring include family members?

Yes, if it is part of the agreed scope. Family members are often targeted for personal information, so many principals include them.

Is the engagement confidential?

Yes. Every engagement is confidential, and we never identify the people we protect.

How do we get started?

Call us or request a confidential consultation. We discuss the principal’s profile, current concerns and who needs to be alerted, then propose a monitoring scope and briefing schedule.
Executive online threat monitoring builds on our OSINT and online investigations and dark web investigations. When harassment or a compromised device is involved, see cyber harassment investigations, hacked phone and computer checks and counter surveillance, or read our case studies.

Have a situation you need handled quietly?

Talk to us today. Every conversation is confidential.

Request a Confidential Consultation Call 631-982-4632
Call 631-982-4632